
OT SecuritySolutions
From offline field security operations and AI perimeter protection to controlled attack simulation and compliance evidence support — building deployable, verifiable security capabilities for OT environments.
Industrial cybersecurity awareness is rapidly awakening & transforming
~1.9X Growth
Annual increase in OT attacks
Enterprise Adoption
Actively monitoring OT networks
-
Industrial organizations hit by cyberattacks in the past year
-
Growth in ransomware attacks targeting OT
-
Enterprises lacking full OT network visibility
Attackers are scaling
at unprecedented speed
their attack operations
Complete ProductPortfolio
Every solution maps to real industrial scenarios, covering equipment delivery, OT perimeter protection, attack-defense validation, and compliance audit workflows.

OPS
A portable USB-based device designed for offline malware scanning, encrypted file transfer, and system health checks. It helps equipment manufacturers, maintenance teams, and controlled environments establish trusted OT security workflows during delivery and maintenance.

AI IPS
Powered by the Nvidia AI core hardware and software platform, combining AI anomaly detection with industrial protocol protection to provide real-time blocking, traffic monitoring, and compliance support for semiconductor and critical manufacturing environments.
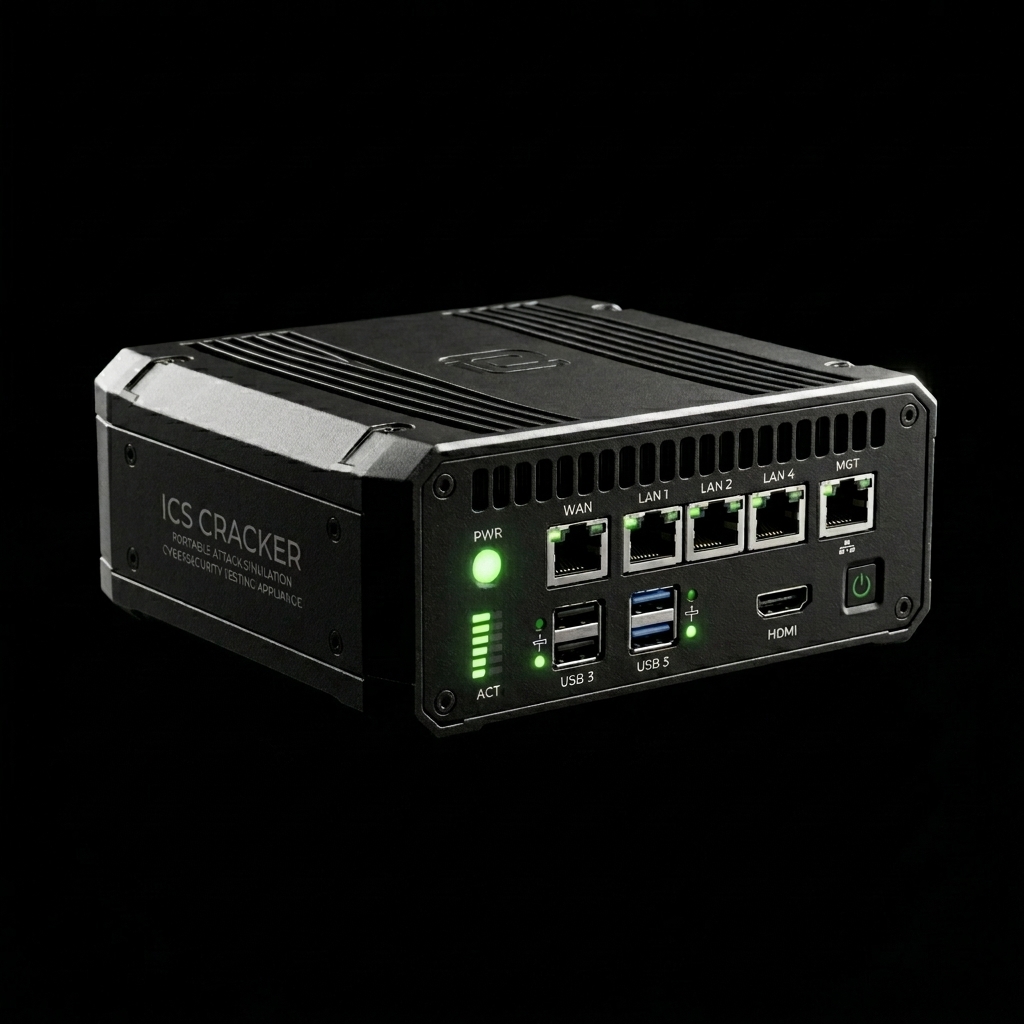
ICSCracker
Built on a ruggedized industrial hardware platform as its validation carrier, it performs controlled industrial attack simulations and verification tests. It helps product teams and factories validate OT protection effectiveness and supports evidence collection requirements for IEC 62443, CRA, and SEMI E187.
IEC 62443 Consulting
For ICS vendors: build the secure development lifecycle IEC 62443-4-1 requires, implement the component security requirements of IEC 62443-4-2, and prepare the documentation and test evidence third-party certification requires.
EU CRA Consulting
Helping manufacturers of products with digital elements sold in the EU meet the Cyber Resilience Act (EU 2024/2847): product classification, gap analysis against the essential requirements, SBOM and vulnerability handling, incident reporting, and conformity assessment and technical documentation.
QuantifiedSecurity Impact
OPS, AI IPS, ICSCracker & ICS Checker — connecting protection, validation, and compliance.
Supporting IEC 62443, CRA, NIST, DNV, UAV & SEMI E187 validation and evidence preparation.
OT cybersecurity validation environments supporting attack simulation, compliance testing, and evidence generation.
ProductAdvantages
Purpose-designed for industrial environments, balancing security and availability. Not IT solutions forced onto OT — built from the ground up for industrial scenarios.
Designed for OT Environments
Supports mainstream ICS protocols without impacting real-time requirements, ensuring continuous production.
Easy Deployment
Deploy without downtime — passive monitoring doesn't affect existing network architecture.
Localized Service
Traditional Chinese interface with local technical teams who deeply understand Taiwan's industry regulations.
Integrated Solutions
Products are highly integrated with each other and seamlessly connect with existing IT security infrastructure.
Common questions
What teams ask before the first meeting
How do OPS, AI IPS and ICSCracker differ, and where should we start?
They map to three stages. OPS is a portable USB device for offline endpoints — malware scanning, encrypted file exchange and device health checks where there is no network. AI IPS is the industrial intrusion prevention system on the OT perimeter, pairing AI anomaly detection with a signature engine, deployable inline or in monitoring mode. ICSCracker is the attack simulation engine that verifies whether any of it actually holds. When the goal is a compliance audit, most engagements start with an ICSCracker baseline: find the gaps first, then decide on protection.
Will attack simulation disrupt a running production line?
It never runs against live production. Every attack operation happens in a controlled OT security lab or an isolated segment, physically separated from production and from the enterprise IT network (MES, ERP, internet), and no destructive testing is performed on production equipment. The platform runs standalone and fully offline, with built-in Modbus and SECS/GEM simulators so a team can rehearse without the real device present.
Which industrial protocols are supported?
Industrial protocols cover Modbus TCP, OPC UA, S7comm and EtherNet/IP; IIoT and semiconductor environments add MQTT and SECS/GEM; the general service surface covers SSH, HTTP/HTTPS, SNMP, Telnet and DNS. Attack scenarios include unauthorised register writes, malformed control-command injection and denial-of-service testing.
Which standards and regulations does this map to?
IEC 62443 (including the SVV-3 / SVV-4 verification items), the EU Cyber Resilience Act, SEMI E187, NIST CSF, and DNV and UAV requirements. Findings are mapped automatically onto MITRE ATT&CK for ICS, CWE and OWASP, then organised into each standard's audit items — no manual cross-referencing afterwards.
What do we receive when testing finishes?
A structured IEC 62443 Security Verification & Validation report, exportable as HTML or PDF, stating the product and version under test, the standard applied, the pass/completion rate, per-item results with evidence, plus a compliance evidence package mapped to the regulation clauses and a findings summary. After remediation the same test cases re-run, so improvement is measured against the same baseline.
How does a consultation start — do we have to hand over internal data?
No sensitive data is required. The first step is a 30-minute online consultation with an IEC 62443-certified engineer to identify the largest risk in the current OT environment and a workable order of remediation, followed by written recommendations within five working days. Whether to proceed to hands-on testing is decided after that.
Need a Custom Solution?
Every industrial environment is unique. Contact our expert team to craft the most suitable security solution for you.